
Session Fixation in osTicket v1.18.2
La aplicación mantiene activo el identificador de sesión inicial (OSTSESSID) tras un login correcto, lo que permite a un atacante secuestrar la cuenta de la víctima.
CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:A/VC:L/VI:L/VA:N/SC:N/SI:N/SA:N
Background
osTicket by Enhancesoft, a free and open-source technical support ticket management system.
Description
A session fixation vulnerability exists in osTicket v1.18.2. The application assigns a session cookie (OSTSESSID) to unauthenticated users and does not regenerate this identifier after a successful login. As a result, the pre-authentication session token is promoted to an authenticated context without being replaced.
An attacker who can set or predict the victim's OSTSESSID value before login — for example, via a crafted link or a cross-site scripting vector — can reuse that same cookie to access the victim's authenticated session, gaining full control over the account.
Proof of concept
The initial cookie OSTSESSID with the value POC-COOKIE is a guest-user context cookie, i.e. not authenticated.
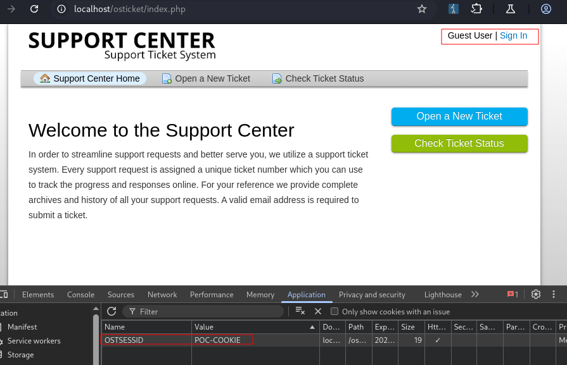
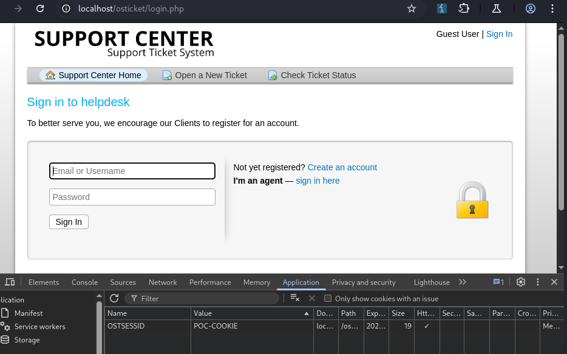
We access the login panel:
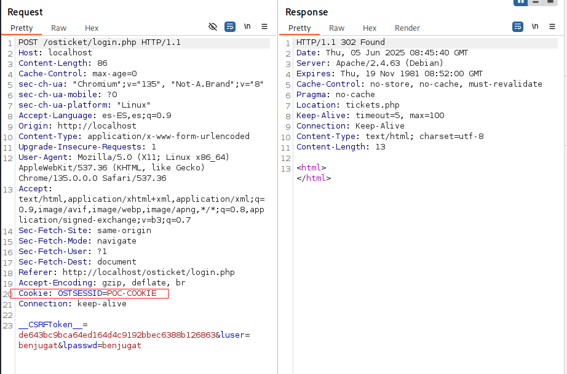
And we log in. As shown in the server response, it does not set any new cookie for the authenticated context.
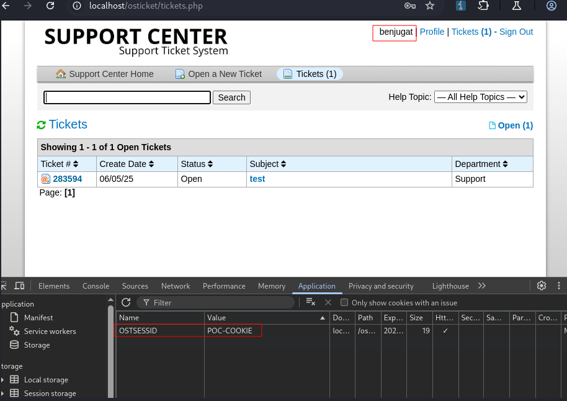
Finally, we are correctly logged in as the user benjugat and the cookie has not been replaced, it keeps the initial POC-COOKIE value. The server has simply promoted it from unauthenticated to authenticated context.
Business impact
An attacker capable of fixing the session identifier before the victim logs in can hijack the authenticated session, gaining full access to the victim's account. This can lead to unauthorized access to support tickets, customer data exposure, and potential privilege escalation within the helpdesk system.
Systems affected
osTicket v1.18.2
Solution
The osTicket project has been placed in maintenance mode by Enhancesoft. Users are advised to monitor the official repository for updates and apply any future patches that regenerate the session identifier upon successful authentication.
Disclosure timeline
References
The information contained within this advisory is supplied 'as-is' with no warranties or guarantees of fitness of use or otherwise. Internet Security Auditors accepts no responsibility for any damage caused by the use or misuse of this information.
Compañía con sede en España y Colombia, especializada en auditoría de aplicaciones web, seguridad de red, test de intrusión e implantación y evaluación de cumplimiento. Nuestros clientes incluyen algunas de las mayores compañías de finanzas, telecomunicaciones, seguros y TIC. Proveedor independiente de fabricante, con experiencia profunda desde 2001. Nuestro esfuerzo en I+D incluye investigación de vulnerabilidades, colaboración en proyectos abiertos de seguridad, whitepapers y participación en eventos del sector.
¿Quieres que revisemos tu producto?
Contacta con nosotros¿Necesitas una auditoría de seguridad?
Cuéntanos tu situación y nuestro equipo se pondrá en contacto contigo para orientarte o agendar una llamada técnica.