
Session Fixation in osTicket v1.18.2
The application keeps the initial session identifier (OSTSESSID) active after a successful login, which allows an attacker to hijack the victim's account.
CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:A/VC:L/VI:L/VA:N/SC:N/SI:N/SA:N
Antecedentes
osTicket by Enhancesoft, a free and open-source technical support ticket management system.
Description
A session fixation vulnerability exists in osTicket v1.18.2. The application assigns a session cookie (OSTSESSID) to unauthenticated users and does not regenerate this identifier after a successful login. As a result, the pre-authentication session token is promoted to an authenticated context without being replaced.
An attacker who can set or predict the victim's OSTSESSID value before login — for example, via a crafted link or a cross-site scripting vector — can reuse that same cookie to access the victim's authenticated session, gaining full control over the account.
Prueba de concepto
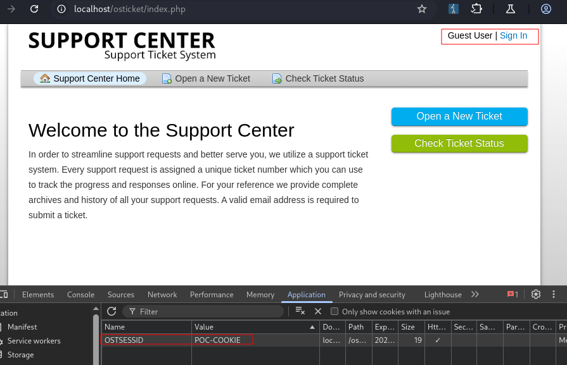
The initial cookie OSTSESSID with the value POC-COOKIE is a guest-user context cookie, i.e. not authenticated.
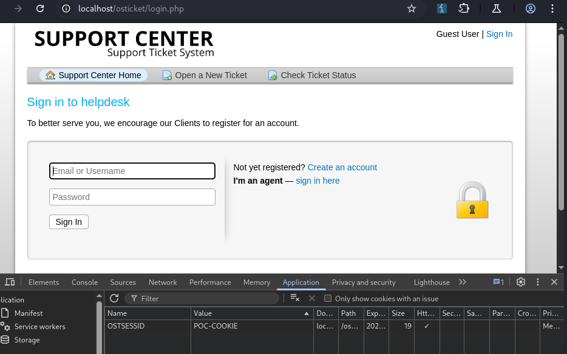
We access the login panel:
Y procedemos a iniciar sesión. Como se muestra en la respuesta del servidor, no establece ninguna cookie nueva para el contexto autenticado.
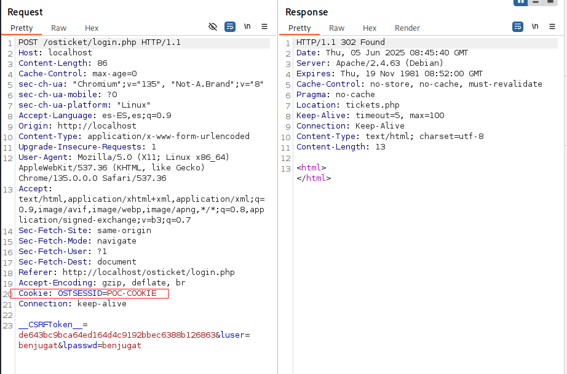
Finalmente, hemos iniciado sesión correctamente como el usuario benjugat y la cookie no ha sido reemplazada, mantiene el valor inicial de POC-COOKIE. El servidor simplemente la ha promovido de un contexto no autenticado a uno autenticado.
Business impact
An attacker capable of fixing the session identifier before the victim logs in can hijack the authenticated session, gaining full access to the victim's account. This can lead to unauthorized access to support tickets, customer data exposure, and potential privilege escalation within the helpdesk system.
Sistemas afectados
osTicket v1.18.2
Solución
El proyecto osTicket ha sido puesto en modo de mantenimiento por Enhancesoft. Se aconseja a los usuarios monitorear el repositorio oficial para obtener actualizaciones y aplicar cualquier parche futuro que regenere el identificador de sesión tras una autenticación exitosa.
Calendario de divulgación
References
The information contained within this advisory is supplied 'as-is' with no warranties or guarantees of fitness of use or otherwise. Internet Security Auditors accepts no responsibility for any damage caused by the use or misuse of this information.
Company based in Spain and Colombia, specializing in web application auditing, network security, penetration testing, and compliance implementation and assessment. Our clients include some of the largest finance, telecommunications, insurance, and ICT companies. A vendor-independent provider with deep expertise since 2001. Our R&D efforts include vulnerability research, collaboration on open security projects, whitepapers, and participation in industry events.
Would you like us to review your product?
Contact usDo you need a security audit?
Tell us about your situation and our team will get in touch with you to provide guidance or schedule a technical call.
Request information
Our offices
Transversal 22 # 98-82, Porta 100 Building, Office 1003
110221 Bogotá (Colombia)